★ Medical Billing Services Starting as Low as 2.5% of Collections*

HIPAA Compliance Statement

Protecting Patient Information Is at the Core of Everything We Do

At SaMeD RCM Solutions LLC, protecting the privacy and security of patient information is an essential part of our Revenue Cycle Management services.

When our services involve access to Protected Health Information (PHI) or electronic Protected Health Information (ePHI), we maintain administrative, technical, and physical safeguards designed to protect the confidentiality, integrity, and availability of that information and to support compliance with applicable requirements of the Health Insurance Portability and Accountability Act (HIPAA).

Our commitment extends throughout the revenue cycle, from billing and claims processing to payment posting, denial management, accounts receivable follow-up, credentialing support, and other services involving authorized access to healthcare information.

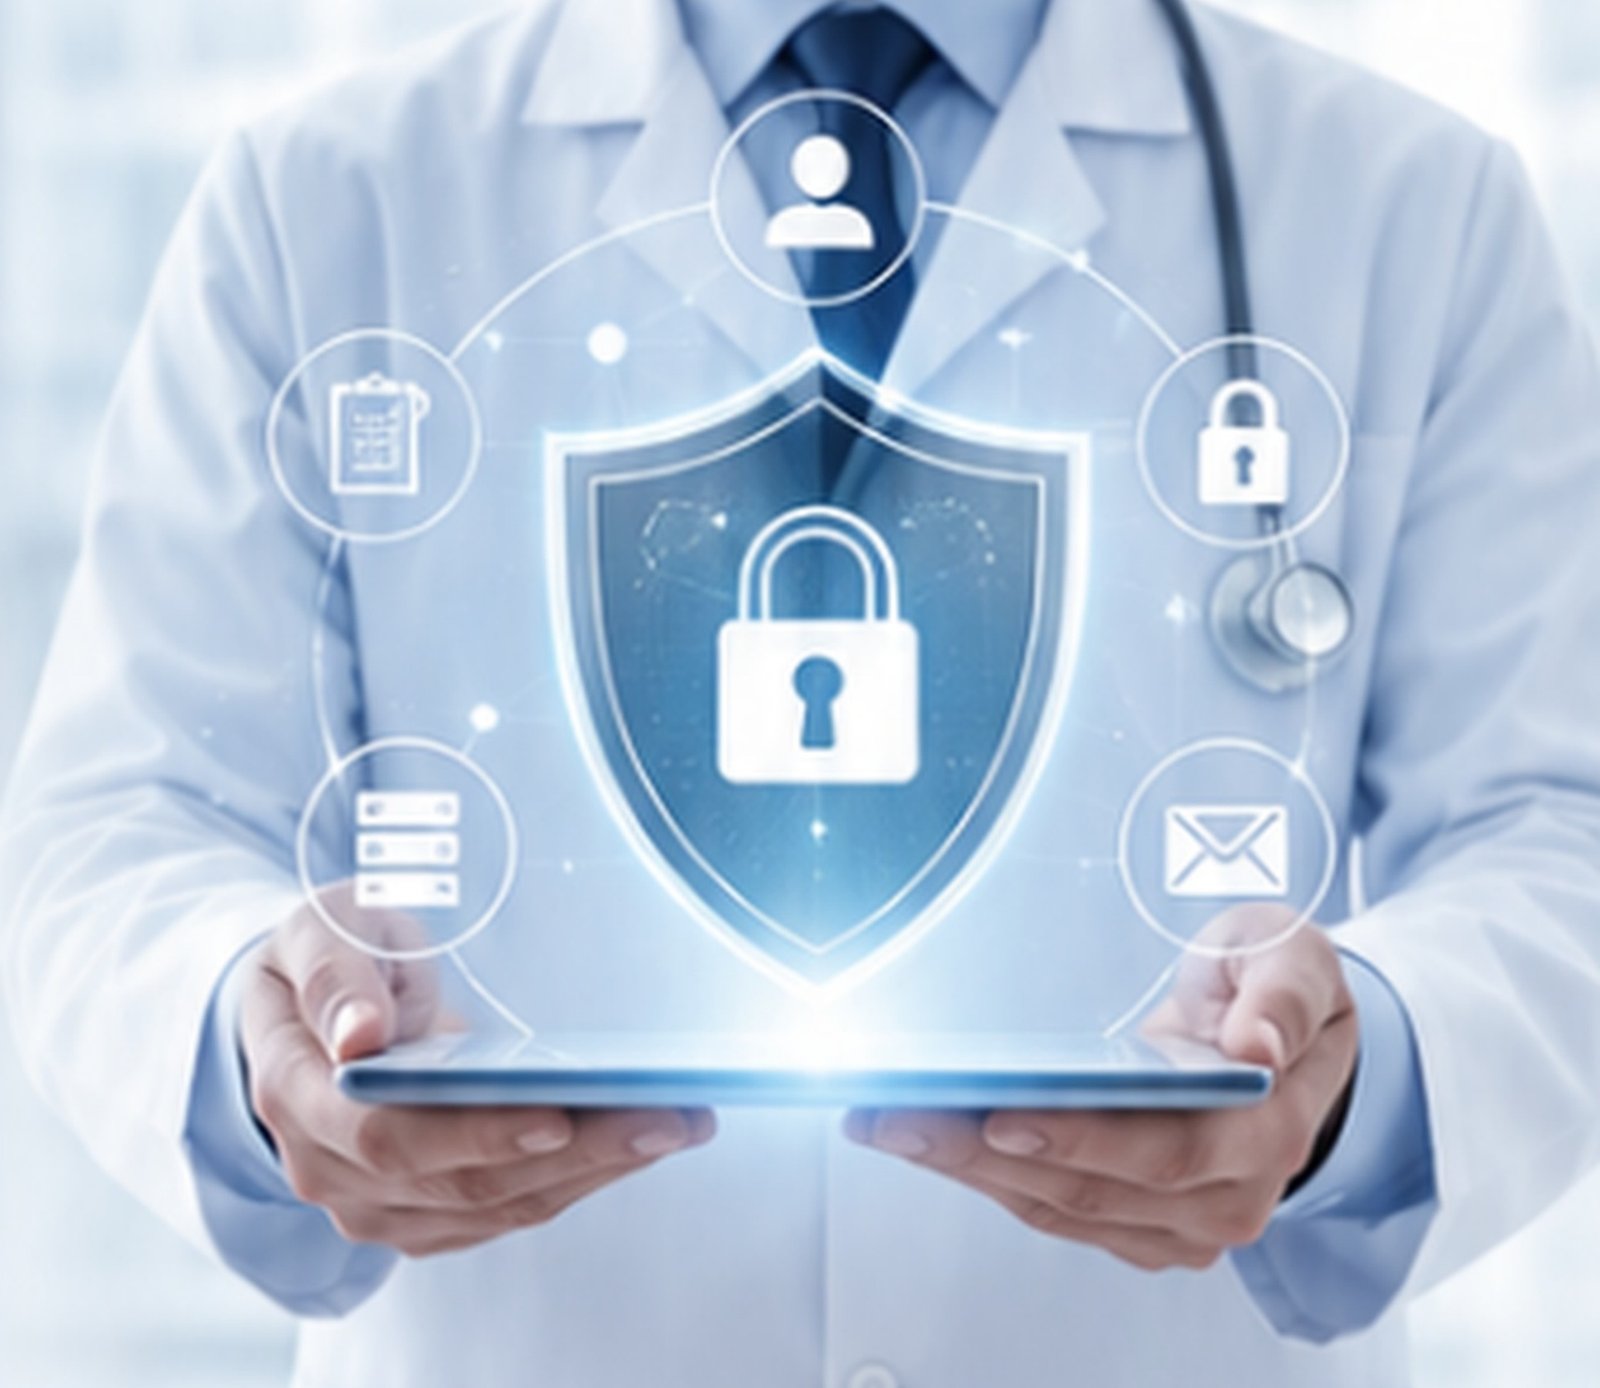
Doctor holding a tablet with a security shield and padlock, surrounded by patient record, lock, server and email symbols

1.Our HIPAA Commitment

SaMeD RCM Solutions LLC is committed to responsible handling of PHI and ePHI.

Our privacy and security program is designed to support:

  • Confidential handling of patient information
  • Appropriate access to PHI based on job responsibilities
  • Protection against unauthorized access, use, or disclosure
  • Secure handling and transmission of sensitive information
  • Workforce privacy and security awareness
  • Appropriate response to suspected privacy or security incidents
  • Ongoing review of privacy and security practices
  • Compliance with applicable Business Associate Agreement requirements
2.Administrative, Technical & Physical Safeguards

Administrative Safeguards

  • HIPAA privacy and security awareness training
  • Workforce confidentiality requirements
  • Role-based information access
  • Information security and risk-management procedures
  • Access management practices
  • Privacy and security policies
  • Security incident response procedures
  • Periodic review of security practices
  • Appropriate Business Associate Agreements

Access to PHI is limited to authorized personnel based on their assigned responsibilities and applicable minimum necessary requirements.

Technical Safeguards

  • Secure user authentication
  • Access controls and system permissions
  • Secure methods for transmitting sensitive information
  • Protection of authorized devices and workstations
  • Access monitoring where available
  • Security controls provided through authorized EHR, Practice Management, billing, and communication platforms
  • Endpoint and system security measures

Access to client systems is limited to personnel who require access to perform authorized services.

Physical Safeguards

  • Workstation security
  • Device protection
  • Authorized workspace access
  • Secure handling of confidential information
  • Appropriate disposal of sensitive information and media

3.Workforce Privacy & Confidentiality

Personnel who may access PHI or ePHI are expected to follow our privacy, confidentiality, and information-security requirements. Privacy and security awareness may include proper handling of PHI and ePHI, confidential communication practices, password and account security, phishing and cybersecurity awareness, secure document handling, and reporting suspected privacy or security incidents. Team members are expected to access patient information only when necessary to perform their authorized responsibilities.

4.Business Associate Agreements (BAA)

When SaMeD RCM Solutions LLC performs services that make us a Business Associate under HIPAA, we enter into an appropriate Business Associate Agreement (BAA) with the Covered Entity or other applicable Business Associate. The BAA establishes responsibilities regarding the permitted use and disclosure of PHI, safeguarding of information, incident and breach reporting, and other applicable HIPAA obligations. Where applicable, subcontractors or service providers that create, receive, maintain, or transmit PHI on our behalf are also required to meet appropriate privacy, security, and contractual requirements.

5.Security Incident & Breach Response

SaMeD RCM Solutions LLC maintains procedures for responding to suspected privacy or security incidents involving PHI. When an incident requires notification under HIPAA or an applicable Business Associate Agreement, we work with the affected client and follow applicable reporting and response requirements. We also review relevant incidents to identify opportunities to strengthen our privacy and security practices.

6.Continuous Compliance & Security Improvement

Protecting healthcare information requires ongoing attention. We periodically review our privacy, security, and operational practices to maintain appropriate safeguards and support applicable requirements of the:

  • HIPAA Privacy Rule
  • HIPAA Security Rule
  • HIPAA Breach Notification Rule
  • Applicable provisions of the HITECH Act
  • Applicable federal requirements
  • Relevant Business Associate Agreements

We also monitor changes in healthcare privacy and cybersecurity requirements and update our policies and practices when appropriate.

7.Shared Responsibility

SaMeD RCM Solutions LLC works with healthcare providers to support secure and responsible revenue cycle operations. Each Covered Entity remains responsible for its own HIPAA obligations, including its internal policies, workforce practices, systems, access controls, patient privacy responsibilities, and other compliance requirements applicable to its organization. We work collaboratively with our clients to support secure information handling throughout the services we provide.

8.Important Compliance Notice

SaMeD RCM Solutions LLC maintains policies, procedures, and safeguards designed to meet applicable HIPAA requirements associated with the services we perform. The U.S. Department of Health and Human Services (HHS) and its Office for Civil Rights (OCR) do not provide an official certification of organizations, persons, or products as “HIPAA compliant.” Accordingly, compliance depends on an organization’s actual policies, safeguards, practices, contractual obligations, and ongoing adherence to applicable HIPAA requirements. No information-security system can eliminate all risk. We therefore continuously review and improve our privacy and security practices as technologies, risks, and regulatory requirements evolve.

SaMeD RCM Solutions team member

Questions About HIPAA or Business Associate Agreements?

Our team is available to discuss privacy, security, and BAA-related questions.

SaMeD RCM Solutions LLC